Latest Updates and Insights on WordPress Security
WordPress Comment2Shell Vulnerability Lets Hackers Take Over Sites Through Comments
25 September 2026
 WordPress administrators are being urged to patch a high-severity core vulnerability that can turn an anonymous comment into server-side command execution. Tracked as CVE-2026-93485 and demonstrated by the Comment2Shell proof-of-concept, the flaw is an unauthenticated stored cross-site scripting issue in WordPress’s wpautop() formatting function. WordPress fixed the vulnerability in version 7.1.1 and advised site owners […]
The post WordPress Comment2Shell Vulnerability Lets Hackers Take Over Sites Through Comments appeared first on Cyber Security News.
Hackers Actively Exploiting WordPress Vulnerability to Execute Malicious Code
25 September 2026
 The critical WordPress vulnerability CVE-2026-87902 is being actively exploited, with activity progressing from reconnaissance to attempts to write malicious PHP files on vulnerable servers. The flaw affects WordPress Core versions 4.7.0 through 7.1.1 and has been fixed in WordPress 7.1.2 and backported releases. Patchstack researchers reported that exploitation began on September 22, shortly after the […]
The post Hackers Actively Exploiting WordPress Vulnerability to Execute Malicious Code appeared first on Cyber Security News.
Attackers Exploit WordPress CVE-2026-87902 Within Hours of Disclosure
24 September 2026
Threat actors have begun to actively exploit a critical security flaw in WordPress within hours of public disclosure.
The vulnerability in question is CVE-2026-87902 (CVSS score: 9.2), which could allow an unauthenticated attacker to obtain remote code execution (RCE).
"An unauthenticated attacker can make get_page_template() page-template resolution include a chosen readable local .php file
Critical WordPress Core Vulnerability Lets Attackers Execute Code Without Logging In
23 September 2026
 WordPress has released version 7.1.2 to address a critical security vulnerability that could allow unauthenticated attackers to execute code on vulnerable websites under specific conditions. Site administrators should update immediately because successful exploitation may not require attackers to log in or have a valid WordPress account. The flaw is tracked as CVE-2026-87902, and it affects […]
The post Critical WordPress Core Vulnerability Lets Attackers Execute Code Without Logging In appeared first on Cyber Security News.
WordPress Malware Uses Hidden Plugin and Blockchain C2 to Stay Undetected
23 September 2026
 A newly identified WordPress malware strain is using a hidden plugin, stolen administrator access, and a blockchain-based command channel to remain active on compromised websites. The threat is built to survive common cleanup efforts while quietly collecting sensitive data from affected servers. The malware is installed as a must-use plugin, a type of WordPress component […]
The post WordPress Malware Uses Hidden Plugin and Blockchain C2 to Stay Undetected appeared first on Cyber Security News.
WordPress Issues Patch for Critical Flaw That Can Enable Code Execution on Some Servers
22 September 2026
WordPress has fixed a critical flaw in its core software that lets an attacker with no account make a site load a PHP file from outside its theme folders.
On some servers, that can go further, allowing the attacker to run their own code. The fix shipped on September 22 in WordPress 7.1.2, with fixes for every branch the project still supports, back to 4.7, and WordPress is telling site owners
WordPress 7.1.2 Release
22 September 2026
This security release features a fix for a critical severity security vulnerability. Because this is a security release, it is recommended that you update your sites immediately. You can download WordPress 7.1.2 from WordPress.org, or visit your WordPress Dashboard, click “Updates”, and then click “Update Now”. If you have sites that support automatic background updates, […]
Hackers Exploit WordPress Flaws to Steal 18,566 Government Records and Plaintext Passwords
22 September 2026
 A suspected Chinese-speaking threat actor has used WordPress vulnerabilities to break into at least 49 organizations across 29 countries. The campaign exposed how a compromised website can become a launchpad for database theft, credential abuse, and wider network intrusion. The attackers exploited the wp2shell chain, tracked as CVE-2026-63030 and CVE-2026-60137, against vulnerable WordPress installations. After […]
The post Hackers Exploit WordPress Flaws to Steal 18,566 Government Records and Plaintext Passwords appeared first on Cyber Security News.
WordPress Comment2Shell Flaw Can Turn Anonymous Comment XSS Into RCE via Admin Session
22 September 2026
A new flaw in WordPress core let an anonymous visitor leave a comment that planted a hidden script on the page. If a logged-in administrator later opened that page, the script could run code on the site's server.
WordPress fixed the flaw, tracked as CVE-2026-93485 and dubbed "Comment2Shell," on September 17 in version 7.1.1 and told site owners to update right away. There is
Click2Shell WordPress Flaw Lets Attackers Gain RCE With a Single Malicious Link
19 September 2026
 WordPress administrators are being urged to update after researchers disclosed Click2Shell, an exploit chain that can turn one malicious link into remote code execution (RCE) on a vulnerable website. The issue begins with a WordPress Core theme-preview weakness that silently installs an attacker-selected theme from the official directory, then becomes a server compromise when chained […]
The post Click2Shell WordPress Flaw Lets Attackers Gain RCE With a Single Malicious Link appeared first on Cyber Security News.
New WordPress Click2Shell Flaw Forces Theme Installs, Can Chain to Code Execution
18 September 2026
WordPress today released patches to fix a new set of vulnerabilities in its core software, one of which could allow a crafted web link, opened by a logged-in administrator, to install a theme from the official WordPress.org directory without anyone clicking Install.
The security firm pwn.ai, whose researchers reported the flaw, calls the attack chain Click2Shell. On its own the flaw only
Tutor LMS Flaw Exposes 100,000+ WordPress Sites to Remote Code Execution
18 September 2026
 A high-severity flaw in the Tutor LMS WordPress plugin could let a low-privileged user take control of an affected server. The issue affects more than 100,000 sites that use the e-learning plugin, particularly installations that allow visitors to register as students. Tracked as CVE-2026-78175, the vulnerability is rated 8.8 out of 10 and affects Tutor […]
The post Tutor LMS Flaw Exposes 100,000+ WordPress Sites to Remote Code Execution appeared first on Cyber Security News.
Brevo Supply Chain Attack Pushes WordPress Backdoors and ClickFix Malware to 100,000+ Sites
18 September 2026
 A supply-chain compromise involving Brevo briefly turned widely used website tools into a delivery channel for malware. Attackers inserted hostile JavaScript into services that customer websites load, exposing both visitors and WordPress administrators. The activity reached more than 100,000 customer sites on September 14, according to the investigation. People who opened affected sites, chat features, […]
The post Brevo Supply Chain Attack Pushes WordPress Backdoors and ClickFix Malware to 100,000+ Sites appeared first on Cyber Security News.
WordPress Urges Immediate Update After Fixing 11 Security Vulnerabilities
18 September 2026
 WordPress has released version 7.1.1, a security and maintenance update that fixes 11 vulnerabilities affecting the widely used content management system. Website owners and administrators are urged to install the update immediately to reduce the risk of cross-site scripting, authorization bypass, information disclosure, path traversal, and content manipulation attacks. The WordPress 7.1.1 release also includes […]
The post WordPress Urges Immediate Update After Fixing 11 Security Vulnerabilities appeared first on Cyber Security News.
WordPress 7.1.1 Maintenance and Security Release
17 September 2026
This security and maintenance release features 17 bug fixes on Core, 19 bug fixes for the Block Editor, and 11 security fixes. Because this is a security release, it is recommended that you update your sites immediately. You can download WordPress 7.1.1 from WordPress.org, or visit your WordPress Dashboard, click “Updates”, and then click “Update […]
Hackers Exploit WooCommerce Plugin Bug to Take Over WordPress Sites Without Login
15 September 2026
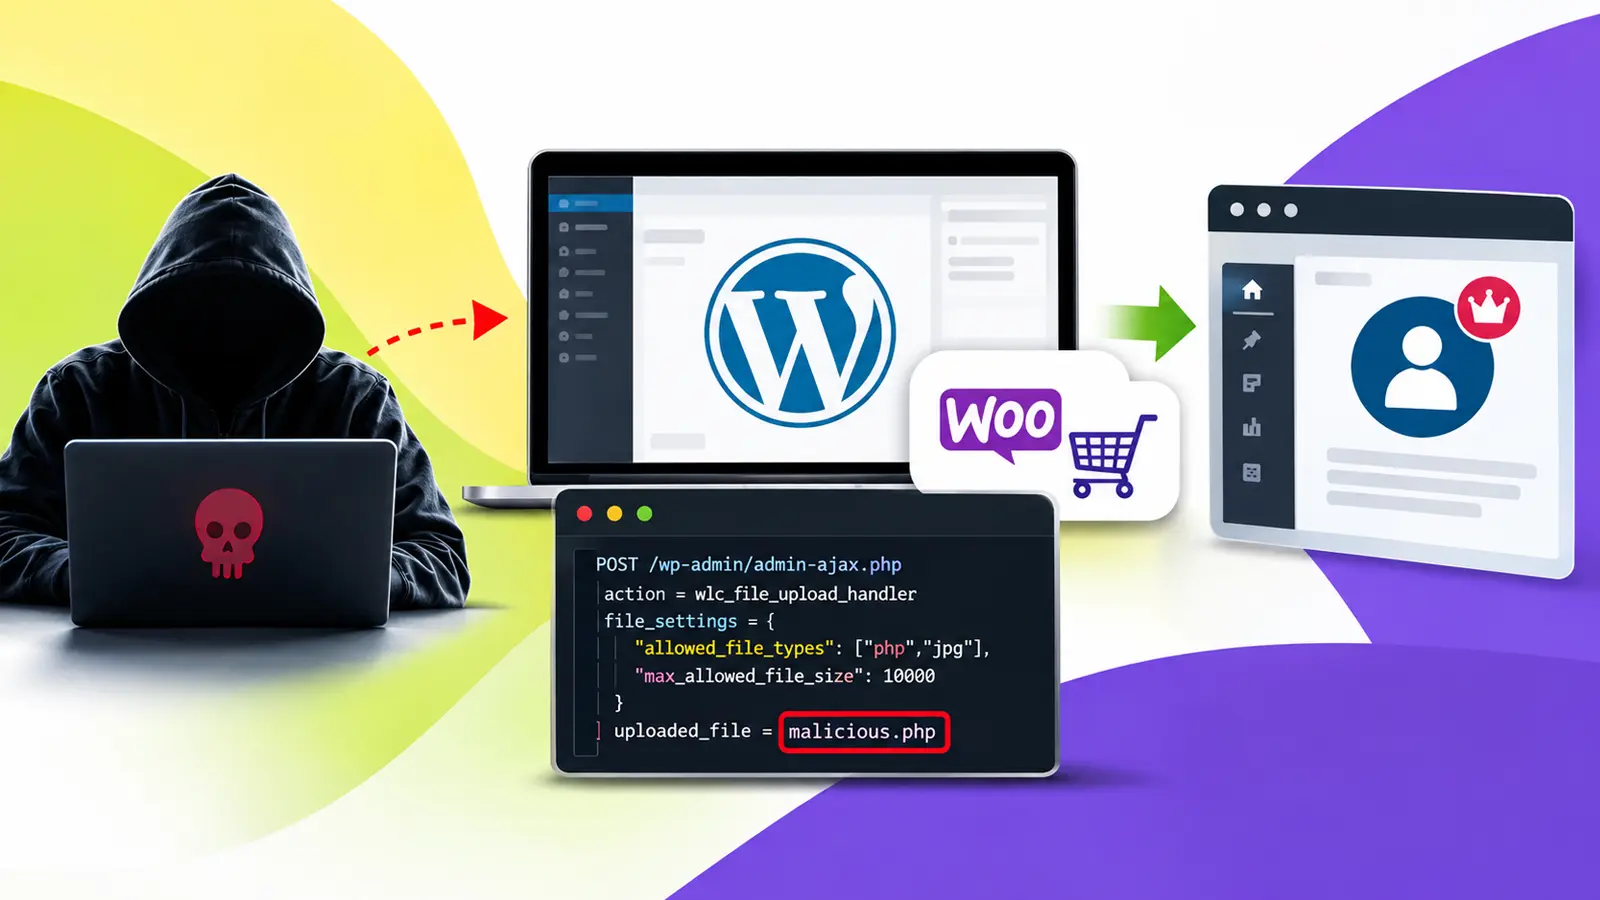 Attackers are actively exploiting a critical flaw in a WooCommerce extension to seize control of WordPress sites without a username or password. The issue affects Wholesale Lead Capture and turns a routine file-upload feature into a direct path to server access. The vulnerability, tracked as CVE-2026-27540, has a CVSS severity score of 9.8 and affects […]
The post Hackers Exploit WooCommerce Plugin Bug to Take Over WordPress Sites Without Login appeared first on Cyber Security News.
Critical WordPress Plugin Flaws Put Over 600,000 Websites at Risk of Takeover
15 September 2026
 Two critical vulnerabilities in The Events Calendar WordPress plugin could allow unauthenticated attackers to take over vulnerable websites. The flaws affect more than 600,000 active installations. They can lead to remote code execution, administrator password resets, malware deployment, and full server compromise. Wordfence Argus, developed by the Wordfence Threat Intelligence team, discovered the two independent […]
The post Critical WordPress Plugin Flaws Put Over 600,000 Websites at Risk of Takeover appeared first on Cyber Security News.
WordPress Adds Automated Plugin Reviews to Block High-Risk Updates Before Distribution
14 September 2026
WordPress has announced it's launching an automated security review for every release of a plugin before it's distributed through the WordPress.org update API so as to analyze it for potential security issues and ensure there are no risks involved.
"New plugins are reviewed before they enter the directory, but updates ship continuously after that," David Perez, WordPress Official Plugin
WordPress Uses AI to Stop Malicious Plugin Updates Before They Reach Millions of Websites
10 September 2026
 WordPress has rolled out an automated, AI-driven security review that screens every plugin release before it reaches the WordPress.org update API, adding a critical checkpoint to a distribution pipeline that had previously lacked one. The move follows a real-world incident in which a backdoor was slipped into an update for a plugin with roughly 20,000 […]
The post WordPress Uses AI to Stop Malicious Plugin Updates Before They Reach Millions of Websites appeared first on Cyber Security News.
WordPress Plugin Flaw Exposes 5 Million Sites to SQL Injection Attacks
03 September 2026
 A high-severity vulnerability in the All-in-One WP Migration and Backup plugin could allow unauthenticated attackers to take over vulnerable WordPress sites. The flaw, tracked as CVE-2026-19949, affects more than 5 million active installations and has been fixed in version 7.110. The issue was reported to Wordfence on August 14, 2026, by security researcher Jack Taylor […]
The post WordPress Plugin Flaw Exposes 5 Million Sites to SQL Injection Attacks appeared first on Cyber Security News.